
 Open web. Clear feed.

env zero enables platform teams to deliver infrastructure 10x faster without losing control, with standardized, governed workflows at the speed and scale of AI.
Anyone who can open a PR against a template repo can change what its env0.yml runs. env zero now lets your org keep that, limit it to verified users, or block repo custom flows entirely. bit.ly/4zJT6DD

A leaked API key works from anywhere. In env zero, a key can now carry its own IP allowlist, so it only works from those addresses. It stacks on your org allowlist. hubs.la/Q04ClcpP0

Today at 1pm ET: live agentic remediation on a real IaC platform. Artem Artyunov finds what failed and what drifted, then applies a fix on camera, with a human signing off before anything changes. hubs.la/Q04CkG-p0

Most failed or drifted environments still get fixed by hand. Tomorrow at 1pm ET, Artem Artyunov points a coding agent at a live IaC platform, finds what broke and applies a safe fix on camera, with the guardrails shown. hubs.la/Q04Ckylm0
Hypothetical: an agent cleaning up security group rules searches the repo, finds no references to one, and deletes it. If a service someone built in the console depended on that rule, the repo had no way to say so. bit.ly/3VEXQLT

Microsoft is retiring Azure DevOps OAuth apps. env zero now connects to Azure DevOps through Microsoft Entra ID. Connections that need the switch are flagged in Organization Settings > VCS, and templates keep working after it. bit.ly/4BlCKm6

EZ Release Weekly - October 16, 2026 #devops #platformengineering #infra... youtu.be/EAu0zZigK7s?si=2snf… via @YouTube
Day two at DevOpsCon NYC. The env zero team is at the booth showing EZ Control: it finds the gap between the cloud you declared and the cloud you actually run, and closes it under policy. Early Access: hubs.la/Q04yKbF50


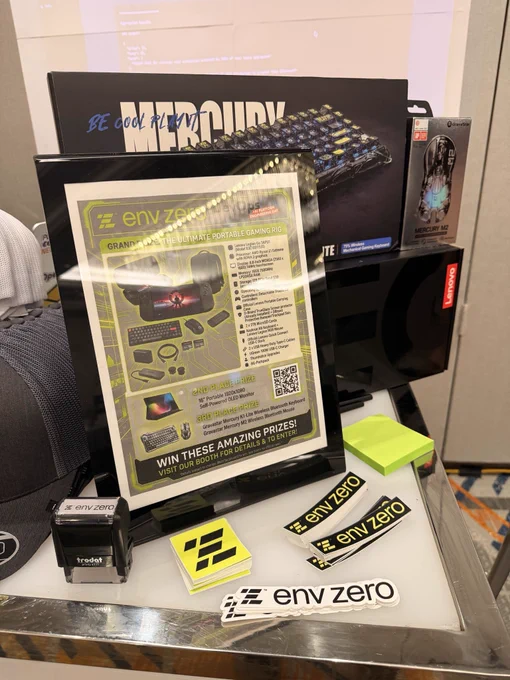
Today, we are at #DevOpsCon & AI Platform Engineering Day New York announcing the Early Access launch of EZ Control, the autonomous cloud control plane for the AI era. EZ Control closes the loop between the state an enterprise intends and the state its cloud is actually in, whether that intent is written as infrastructure code, a rule in a cloud security posture management tool, a policy-as-code repository or a guardrail set within the cloud provider itself. It detects divergence continuously, decides the correct response under policy, and executes the remediation itself. 🗞️ Read the release >> hubs.la/Q04yyhs_0

OIDC credentials in env zero shared one audience claim across AWS, Azure, GCP and Vault, so a token minted for one was replayable against another. v2 issues a provider-specific aud. Opt-in per credential, v1 untouched. hubs.la/Q04xpcSR0
