🇫🇮 ComplexDiscovery's coverage of Slush 2026 in Helsinki is underway!
🎤 Coverage kicked off today with Finnish President Alexander Stubb's opening fireside conversation, addressing artificial intelligence, economic security, data centers, quantum computing and Europe's technology future.
📰 Coming soon: A ComplexDiscovery news analysis of President Stubb's keynote conversation and its implications for cybersecurity, information governance, regulatory compliance and eDiscovery professionals.
🌍 Follow ComplexDiscovery's reporting and analysis throughout Slush week at ComplexDiscovery.com.
#Slush2026#Helsinki#Finland#ArtificialIntelligence#Cybersecurity#InformationGovernance#eDiscovery#ComplexDiscovery
🏦 On Nov. 16, 2026, the Commerce Department’s Bureau of Industry and Security (BIS) released an interim final rule, “Addressing Remote Access to Advanced Semiconductors,” which it said Treasury and the National Security Council wrote and directed. Effective on scheduled Federal Register publication Nov. 19, it requires a license to ship advanced chips, and computers containing them, to any data center worldwide when the shipper knows the facility provides over 12 million “aggregate TPP,” the summed processing performance of covered chips, to companies headquartered or ultimately parented in Macau or Country Group D:5, the U.S. arms-embargoed group that includes China. Shippers are expected to collect each data center’s customer ownership checks, and a data center that will not or cannot supply them is a red flag that presumptively gives the shipper knowledge unless resolved. The rule will also require licenses for Indonesia, Malaysia, Singapore, Thailand and Brazil, except where the ultimate consignee or end user is headquartered or ultimately parented in the United States and the shipper files monthly reports.
💼 For cybersecurity, data privacy, compliance and eDiscovery professionals, its diligence files, notices and reports are records regulators, auditors and litigants may seek. Watch the comment period and the 90-day licensing window.
🔎 Read the complete article from ComplexDiscovery OÜ's artificial intelligence beat at complexd.blog/4zvNZWT.
#ExportControls#BIS#DataCenters#Compliance#eDiscovery#InformationGovernance
🔎 [Editor's Note] From the archive, and still relevant: before you sign off on next year’s event budget, it’s worth asking whether you’re paying for a purpose or for presence.
💼 Legal tech conferences are no longer just industry gatherings—they’re the new corporate boardrooms, performance venues, and marketplaces of influence. In this compelling article, the legal tech landscape is examined with a critical yet constructive lens, illuminating how post-pandemic events have evolved into high-stakes arenas shaped as much by fear as strategy. For professionals in cybersecurity, information governance, and eDiscovery, this piece offers a vital reframing of what these events truly deliver—and what they may be costing in the name of presence.
🛄 By unpacking the motivations, anxieties, and decision-making traps behind sponsorships and attendance, this article prompts a deeper strategic reflection: are your event investments driving value, or simply maintaining visibility? It’s an essential read for leaders who want to reshape their engagement model for maximum impact—not just presence.
📰 Read the complete article from ComplexDiscovery OÜ's eDiscovery beat at complexd.blog/4nbtWGQ.
#LegalTech#eDiscovery#LegalTechEvents#EventStrategy#B2BMarketing#SponsorshipROI#LegalInnovation#ThoughtLeadership#ComplexDiscovery
🪖 At DECOI x Borderland in Helsinki today, the day before Slush, two generals gave early-stage defense startups a clear message about when military buyers start listening.
💡 How it started. FiBAN CEO Tiina Laisi-Puheloinen said DECOI grew out of a question from Gen. Janne Jaakkola, now Finland’s defense chief: where can defense startups go for money? Her answer three years ago was nowhere. This year the hosts said they capped the summit at 500 people and turned away about 300 more.
💶 The money on stage. Business Finland called defense a top strategic priority, and a European Commission official pointed founders to new funding. That’s AGILE, the EU’s 115 million euro defense innovation program for small firms, which expects its first call in early 2027.
🚀 The pitches. Seven startups at readiness levels 4 to 6 had three minutes each. They pitched spectral lidar, drone autonomy, navigation that works when satellite signals are jammed, satellite protection, lighter batteries, acoustic drone detection and counter-drone defense.
🇫🇮 Lt. Gen. Pasi Välimäki, commander of the Finnish Army: development risk belongs to the company because he spends taxpayers’ money, so the army engages from readiness level 7. He described a contract-to-flight timeline measured in months and pointed founders to Arctic Strike 26 testing.
🇺🇸 Retired U.S. Army Gen. Christopher Donahue: test in Ukraine, and plug your data into the shared systems behind NATO’s Eastern Flank Deterrence Initiative.
🛡️ Hybrid threats. Jukka Savolainen of Hybrid CoE explained why attacks kept below the threshold of open war, from disinformation to sabotage, reach well beyond the battlefield.
📂 Why it matters for cybersecurity, information governance and eDiscovery teams. NATO’s vendor requirements read as data obligations. Integration terms and Ukraine field-test records may one day need to be documented, preserved and produced.
🔁 It’s the same question of control we heard at the Tallinn Digital Summit, this time about defense technology.
❓ If military buyers wait for level 7, who funds the companies still at 4, and who governs their data on the way up?
🔗 Read the complete article from ComplexDiscovery OÜ's geopolitics beat at complexd.blog/4AAbA9N.
#DECOIxBorderland#Slush2026#DefenceTech#NATO#HybridThreats#Cybersecurity#InformationGovernance#eDiscovery
🇷🇺 Estonia’s Internal Security Service, known as KAPO, says Russia’s military intelligence agency, the GRU, coordinated an attempted arson attack on drone maker Threod Systems in Viimsi, near Tallinn, early Nov. 14, 2026. Threod’s security team and a joint operation by KAPO and Latvia’s State Security Service, which had passed on warnings beforehand, stopped it. Eight people were detained; prosecutors sought custody for five, and Estonia’s prosecutor general said a court has ordered two of them held.
🇪🇪 On Nov. 15, Estonia’s Foreign Ministry said the government plans to close the country’s road crossings with Russia from Dec. 1, saying the move would curb Russia’s ability to act against Estonia and reduce the risk of sanctions evasion. Russia’s Foreign Ministry spokeswoman said the plan, if real, would be a new outburst of Russophobia. For cybersecurity, information governance and eDiscovery professionals, the case moves physical security, public registry exposure and the preservation of camera footage and access logs into defense-tech diligence.
🔎 Watch whether Estonia makes the closure temporary or indefinite, how the court rules on the remaining custody requests, and whether defense sessions around Slush in Helsinki, Nov. 17 to 19, take up the attack.
📰 Read the complete article from ComplexDiscovery OÜ's geopolitics beat at complexd.blog/3URNTL2.
#Cybersecurity#DefenseTech#Estonia#InformationGovernance#eDiscovery#ComplexDiscovery
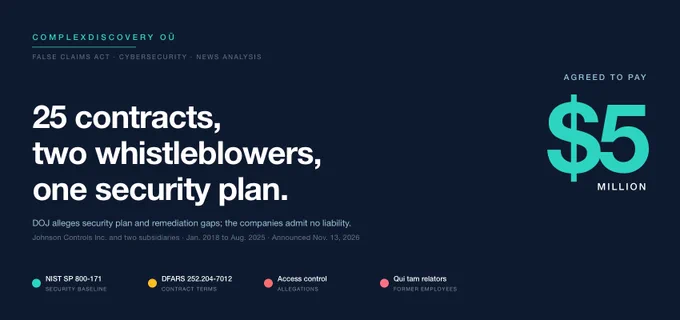
🏦 Johnson Controls Inc. of Milwaukee and two subsidiaries, Johnson Controls Fire Protection LP and Johnson Controls Security Solutions LLC, agreed to pay $5 million to resolve Justice Department allegations, announced Nov. 13, 2026, that from 2018 to 2025 they failed to meet cybersecurity requirements in 25 federal contracts and subcontracts. The government contends the companies did not control access to protected information. For contracts carrying Pentagon procurement rules that require a federal security standard known as NIST SP 800-171, it also contends their system security plan, the document describing how their systems meet that standard, did not fully meet contract terms, and that their plan for fixing gaps was not fully developed or implemented. The agreement says it is not an admission of liability, and the department calls the claims allegations only. The settlement resolves two qui tam suits, in which private citizens sue on the government’s behalf, filed by former employees Kelly Vance and David Thomas; Vance is to receive $850,000.
🔓 For cybersecurity, compliance and eDiscovery professionals, the allegations center on security documentation. Watch the dismissal filings and any agency use of the debarment rights the agreement reserves.
📰 Read the complete article from ComplexDiscovery OÜ's cybersecurity beat at complexd.blog/48rT7jJ.
#Cybersecurity#FalseClaimsAct#GovCon#NIST800171#Whistleblower#InformationGovernance#eDiscovery
🥾 Between the Tallinn Digital Summit and Slush, ComplexDiscovery's event journey took a weekend break with a trip to Rovaniemi. The route ran from Tallinn by Tallink ferry across the Gulf of Finland to Helsinki, then north by overnight train into Lapland and across the Arctic Circle.
🚆 The sleeper train arrived in a city built on a story of recovery. In 1944, retreating German troops burned Rovaniemi during the Lapland War, leaving about 90% of the city destroyed. Alvar Aalto's 1945 reconstruction plan laid out its main roads in the shape of a reindeer's antlers.
🏛️ Arktikum, opened in 1992, was the place to learn the region. It houses the Arctic Centre's science centre and the Regional Museum of Lapland, linked by a 172-meter glass corridor.
🎅 At Santa Claus Village on the Arctic Circle, Santa Claus Main Post Office receives around half a million letters a year from children and adults worldwide. A night trip to Porokari, about 80 kilometers north of the city center along the Ounas River, followed in search of the Northern Lights.
🦌 The last stop was a working reindeer farm about 15 kilometers from Rovaniemi, and it turned out to be a lesson in data management. Every reindeer seen in a Finnish forest belongs to someone, and ownership itself is gated. Only citizens of European Economic Area countries who live permanently in the reindeer herding area may own reindeer, and each owner's earmark must be approved and entered in the Reindeer Herders' Association's register, which holds about 12,000 marks for almost 5,000 owners. Calves receive their owner's mark, cut into the ear, in early summer. The reindeer then roam free across shared pastures for months. At autumn round-ups, herders "read" every earmark to count and register each animal, a legal requirement. A small cut in the fur marks an animal as counted so it is not tallied twice, and reindeer found in another cooperative's area are returned to their own.
💡 The business lesson: information can roam if its ownership travels with it. Decide who may own data, mark it at creation, let it move where the work requires, then round it up on a schedule: read the marks, count once, return what belongs elsewhere and keep the register current. That is information governance, and it is what makes discovery defensible.
🚂 Next comes the train back to Helsinki and preparation for Slush, where the conversation turns from reindeer herds to startup founders and investors.
🧭 The Arctic Circle is a line on a map. Ownership is a mark that travels.
🔎 Learn more about reindeer and reindeer herding from the Reindeer Herders' Association: complexd.blog/4kUqIdn#Rovaniemi#Lapland#InformationGovernance#DataManagement#Slush2026#ComplexDiscovery
✈️ The Federal Aviation Administration (FAA) issued a ground stop covering departures nationwide shortly before 4 p.m. EST on Nov. 13, 2026, and Transportation Secretary Sean Duffy said the airspace reopened at 8:15 p.m., though some international departures were cleared. On Nov. 14, Duffy said officials believe a router flood that began during copper-to-fiber maintenance by contractor L3Harris Technologies at a remote FAA site disrupted aircraft communications and some radar feeds. Officials said they do not believe it was a cyberattack, but Duffy said they have not determined whether installer error or faulty equipment was to blame. L3Harris said it is supporting the FAA investigation; its statement does not address Duffy’s account.
🪪 For cybersecurity, information governance and eDiscovery professionals, the episode shows how a routine change can draw a national security response, why change records and device logs can decide fault, and why early statements ruling out an attack carry risk. In 2023, the FAA kept its attack assessment scoped to the evidence throughout; this week, Microsoft and U.S. officials each began that way and moved to categorical denials within about a day, before any formal root-cause finding. Watch for an FAA root-cause finding and Congress’s funding response.
📰 Read the complete article from ComplexDiscovery OÜ's cybersecurity beat at complexd.blog/4fshQrR.
#FAA#IncidentResponse#ChangeManagement#InformationGovernance#eDiscovery#LitigationHold
🇮🇪 Ireland’s Data Protection Commission (DPC) announced on Nov. 13, 2026, a fine of 11 million euros and a reprimand against MTCH Technology Services Ltd., the Match Group unit behind the Tinder service, and ordered it to make its processing compliant within three months. The DPC found that Tinder’s Download My Data tool, offered as a way for users to get a copy of their personal data, left certain categories out without notice or supplied them only in summary form, breaching Article 15(3) of the EU’s General Data Protection Regulation, which entitles people to a copy of the personal data a company processes about them. Match Group says it has strong defenses and intends to appeal, and court records show MTCH opened High Court proceedings against the DPC on Nov. 6, though not their subject.
🖥️ For cybersecurity, privacy, compliance and eDiscovery professionals, the case shows how a regulator views exports that answer data subject access requests: the DPC’s deputy commissioner said such tools may be partial but must be transparent about how much data they provide. Watch whether the full decision names the omitted categories, how the court case proceeds and pending EU access-request changes.
📰 Read the complete article from ComplexDiscovery OÜ's data privacy and protection beat at complexd.blog/4zmmDSS.
#GDPR#DataPrivacy#DSAR#eDiscovery#InformationGovernance#Compliance
🇫🇮 ComplexDiscovery OÜ and HaystackID (Newsline) will attend Slush 2026, November 18–19, in Helsinki, Finland, with reporting from the event.
🔎 This year’s gathering brings together startup founders, investors, and technology leaders for discussions on building companies, raising capital, and scaling innovation.
📰 Follow along for perspectives on what emerging technologies and investment trends mean for cybersecurity, information governance, and eDiscovery.
👀 Read the latest coverage from ComplexDiscovery OÜ at complexd.blog/2FwUYny.
#Slush2026#Startups#VentureCapital#ArtificialIntelligence#Cybersecurity#InformationGovernance#eDiscovery#ComplexDiscovery
🔐 Workspace software company Notion said Nov. 10 that a dataset affected by a breach at AI inference company Fireworks AI held Notion AI chat transcripts from fewer than 1 percent of Notion workspaces. Notion says Fireworks retained data from the endpoints Notion used despite a contractual commitment to zero data retention; Fireworks’ public bulletins do not address that account. Fireworks said Nov. 9 that its investigation found impacts to billing information and, for a limited set of accounts, to secrets, datasets and incomplete models, and that one intrusion came through a third-party cloud provider hosting its research machines. For the vast majority of affected workspaces, Notion said, the transcripts carried no author or workspace label.
🔎 For cybersecurity, information governance and eDiscovery professionals, the episode shows copies of AI conversations held by an inference provider one tier below the application, under retention promises whose scope differed at each layer.
🖥️ Watch for Fireworks’ further findings, for statements from other customers and for vendors’ answers on which features retain prompts. Legal AI company Harvey was among customers Fireworks told of the hack, The Information reported, and Harvey said none of its customers’ data was affected, according to accounts by MLQ.ai and Sovereign Magazine.
📰 Read the complete article from ComplexDiscovery OÜ's cybersecurity beat at complexd.blog/4C2gxd2.
#eDiscovery#InformationGovernance#Cybersecurity#DataBreach#AIGovernance#LegalTech
📰 Kratt Nation, a discussion paper by an Estonian working group of specialists from Nortal, the University of Tartu, Swedbank and Estonia’s Ministry of Justice and Digital Affairs, plus an independent expert, argues that an AI agent’s limits must be enforced by the systems that receive its actions rather than written into the agent’s instructions.
🗓️ Nortal’s website dates the paper Nov. 4, 2026. It proposes four conditions, including that agents not be given a person’s authentication or signing credentials, and four action classes that scale an agent’s independence to how serious and reversible each step is. The authors say the proposals have not yet been validated as a national model. At the separate Tallinn Digital Summit, held Nov. 5 and 6 in Tallinn, Prime Minister Kristen Michal said Estonia is drafting rules for AI agents.
🖥️ For cybersecurity, information governance and eDiscovery professionals, the paper’s sharpest point concerns evidence: a log shows which channel an action came through but cannot prove who operated the software. Watch Estonia’s draft agent rules and the EU’s revised Product Liability Directive, whose new regime covers products placed on the market or put into service after Dec. 8, 2026.
🔎 Read the complete article from ComplexDiscovery OÜ's artificial intelligence beat at complexd.blog/4eyKNlL.
#KrattNation#AIAgents#TallinnDigitalSummit#InformationGovernance#eDiscovery#Cybersecurity#AIGovernance
🥾 On Pikk Street in Tallinn's Old Town, a medieval merchant's house asks a modern question: what really happens in the garage?
🏛️ The house is home to the People's Museum of Tallinn (Tallinna Rahvaste Muuseum), a branch of the Tallinn City Museum that tells the story of the many peoples who shaped the city's culture. Its current exhibition, "Garaaž. Гараж. Garage," curated by Denis Jatsenko and Aleksandra Ianchenko, treats the garage as a space both private and communal and shows how it became three things at once.
🛡️ First, it was protection for cars. Tallinn's early 20th-century garage buildings and Soviet-era garage areas sheltered the vehicles of a changing city, and the exhibition recalls Estonia's first female drivers among them.
🎨 Then it became a creative den. Workshops, hobby spaces and artists' studios moved in, and artists still make their work in garages today.
💻 Finally, it became an innovation center for entrepreneurs. Businesses still run out of garages, and the exhibition points to the most famous of all: the Palo Alto, California, garage where Bill Hewlett and Dave Packard formed their partnership in 1939, now State Historical Landmark No. 976, the "Birthplace of Silicon Valley."
📜 One of the exhibits presents the "11 Rules of the Garage" that HP formulated, inspired by that garage, on a panel styled like an early computer screen. The list opens with "Believe you can change the world" and closes with a single word: "Invent." Along the way: "Radical ideas are not bad ideas" and "The customer defines a job well done."
🪢 The rules land differently after the Tallinn Digital Summit, which opened with the Estonian folk tale of the kratt, a tireless servant that works as long as it has orders. The advice from the stage: always keep one end of the rope in your own hand. Today's kratt is the AI agent, and the summit spent two days on how to hold that rope. The garage offers the other half of the conversation, why people build at all, and Rule 9 connects the two: "Make a contribution every day. If it doesn't contribute, it doesn't leave the garage."
🚀 The next destination on ComplexDiscovery's Estonia and Finland conference journey is Slush in Helsinki next week, where thousands of founders will carry the same garage spirit onto a much larger floor.
💡 The business lesson: innovation and control are not opposites, and Rule 9 shows how they work together. Inside the garage, ideas can be radical and unfinished. Before anything leaves, whether a product, a feature or an AI agent, it must answer one question: does it contribute? Rule 6 defines who decides, because the customer, not the builder, defines a job well done.
🧭 From the summit stage to a garage door on Pikk Street, the message holds: build boldly, test honestly and keep one end of the rope in hand.
🔎 Read about the "Garage" exhibit at complexd.blog/3XkEsEu.
#Tallinn#TallinnDigitalSummit#Slush2026#Innovation#Entrepreneurship#ComplexDiscovery
🔓 France on Nov. 9 attributed the Oct. 11 to 12 sabotage of refrigeration controllers at about 700 large French retail sites to Shahid Kaveh, a cyber unit of Iran’s Islamic Revolutionary Guard Corps (IRGC), in a report by the government’s interministerial Cyber Crisis Coordination Center. The attackers set defrost cycles of unlimited duration and switched off temperature alarms, causing food losses and at least 15 fires. Paris prosecutors, investigating since Oct. 12, handed the case to investigating judges and requested international arrest warrants; no charges have been announced. Iran’s foreign ministry rejected the accusation as baseless and one-sided.
💼 For cybersecurity, information governance and eDiscovery professionals, a named state actor changes post-incident work: controller, remote-access and network records held by retailers and contractors may carry the same kinds of traces prosecutors cite, and some insurance market model exclusions give weight to a government’s attribution, though attribution alone does not trigger them. France has not attributed a November wave that hit at least 11 European countries, including its blood service. Watch for EU sanctions on the officers France named, any attribution of the November wave and how insurers treat claims from both.
🖥️ Read the complete article from ComplexDiscovery OÜ's cybersecurity beat at complexd.blog/4fov2Oq.
#Cybersecurity#OTSecurity#ThreatIntelligence#CyberInsurance#eDiscovery#InformationGovernance#ColdChain
🔎 HaystackID, a provider of data, forensic and managed review support for investigations, formally launched Trade Fraud Investigation Discovery Services, available now, on Nov. 10, 2026. It targets companies and outside counsel responding to subpoenas, civil investigative demands and qui tam (whistleblower) matters involving suspected tariff fraud. HaystackID says it tests each customs entry against the invoices, factory and shipping records behind it, with generative artificial intelligence (AI) outputs validated by its experts and counsel.
⚖️ The launch follows the Justice Department’s July report that its Trade Fraud Task Force passed $1 billion in recoveries, penalties, forfeitures and publicly charged losses, a composite that includes allegations. An Oct. 1 internal directive from its National Fraud Enforcement Division lists tariff evasion among four corporate enforcement priorities. The division’s Oct. 20 whistleblower rewards program covers health care fraud and fraud on federal programs and benefits, not trade offenses; a separate Criminal Division pilot covers trade, tariff and customs fraud.
🖥️ For cybersecurity, information governance and eDiscovery professionals, the test is whether entry data, messages and AI tool records can be found, preserved and explained. Watch whether the division extends its new rewards to trade fraud and what the first corporate resolutions require.
📰 Read the complete article from ComplexDiscovery OÜ's eDiscovery beat at complexd.blog/4AjusK0.
#TradeFraud#eDiscovery#FalseClaimsAct#InformationGovernance#Investigations#CustomsCompliance
🇺🇦 Russian, Ukrainian and U.S. negotiators are scheduled to meet in Abu Dhabi on Nov. 10 and 11, the first trilateral session since February, with security guarantees at the top of the agenda.
🖥️ The run-up produced four developments, and each leaves a different question open. Two hacker groups published estimates of up to 450,100 war-related deaths from files they say they took from Rosstat, Russia's statistics agency. Rosstat confirms it was attacked but denies any data leaked, the groups say their counts likely include civilians, and their published figures sit about 56,000 apart because they use different inclusion rules. Ukraine's and Russia's emergency alert apps were both compromised; who breached Ukraine's app rests on Kyiv's attribution to Russia. Bomb hoaxes hit dozens of European flights with no group or state named. Russia also claimed a village that the Institute for the Study of War assesses its forces are very unlikely to control.
🔓 For security, information governance and eDiscovery teams, the lesson is provenance: who counted, what was counted and who can confirm it.
🔎 What verification threshold should a leaked dataset clear before your organization treats it as the record?
📰 Read the complete article from ComplexDiscovery OÜ's geopolitics beat at complexd.blog/4iB3xDu.
#Ukraine#AbuDhabiTalks#Cybersecurity#InformationGovernance#eDiscovery#DataProvenance#HybridThreats#Geopolitics