
Hey friends, we’ve moved to @dryrunsec and invite you to follow us there to stay up-to-date with all of the DryRun Security news and happenings. Hope to see you there!

 Open web. Clear feed.

We believe there is one thing missing from all tools on the market today: security context for developers. DryRun Security provides that context as you code.
Hey friends, we’ve moved to @dryrunsec and invite you to follow us there to stay up-to-date with all of the DryRun Security news and happenings. Hope to see you there!
Still chasing false positives with regex? 😵💫 Our NLCPs treat code as context, not just text—so you catch real risk, fast. See how AppSec teams are spotting auth gaps, insecure workflows & PII leaks 🔍 👇 Read the blog na2.hubs.ly/y0kSB50 #AppSec #DevSecOps #AI
RSVP at 🙋In-person: owasp-austin-2025-june.event… 💻Online: meetup.com/owasp-austin-chap…

SAST is stuck. Regex can’t catch AI-generated logic flaws. Join @wickett at #OWASP Austin to see how context-first security changes the game. Live demo + 2025 SAST Accuracy Report 👇for links to the event #AppSec #SAST #DevSecOps #AI #Cybersecurity

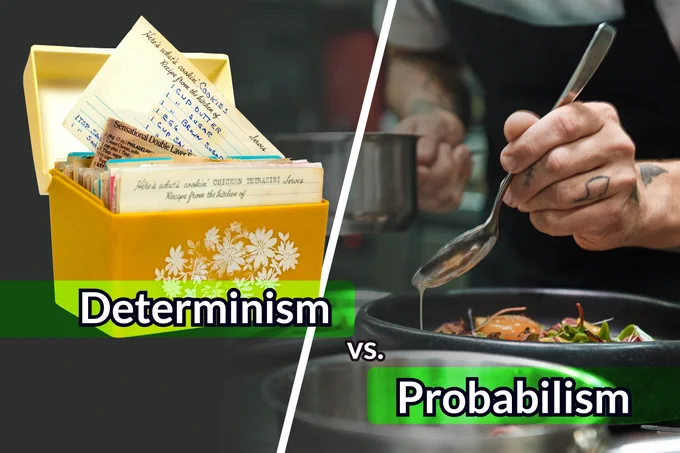
Legacy scanners follow recipes. Probabilism thinks like a chef. 👨🍳 Our latest blog explores probabilistic vs. deterministic SAST—and why rigid rules can’t catch complex, real-world risks. 📖 Read it here: na2.hubs.ly/y0f9Zr0 #AppSec #SAST #AI #Cybersecurity #DevSecOps
Legacy SAST + AI = window unit AC ❄️🪟 AI-native SAST = central air 🌬️🔥 One’s clunky. The other’s seamless, efficient, and built in. We didn’t retrofit—DryRun is AI from the ground up. Full blog 👇 bit.ly/3Hf0LUo #AppSec #SAST #CyberSecurity #AI

New pod drop 🎙️ DryRun CEO, @wickett, joined Oliver Legg of @AspironSearch at RSA to talk blazing-fast SAST accuracy (88% vs ~40% 😳), building DryRun from the ground up, and brisket. TL;DR: Pattern-matching is out. Contextual Security is in. 🔗 bit.ly/4mJ7Dto
A quiet scanner that misses real flaws is worse than one that cries wolf. Chasing low false positives is a distraction. Accuracy is king. 🛡️ Read our take: bit.ly/4jb85hX

3/3 DryRun Security analyzes code context in real-time, catching risks that others overlook. See the full results of our head-to-head test at bit.ly/3FKTBq0

2/3 Contextual Security Analysis keeps outperforming! Legacy tools rely on pattern matching and still miss critical logic flaws.
1/3 It’s the Python/Django edition! This is the third head-to-head assessment against Snyk, CodeQL, Semgrep, and SonarQube. We tested real security flaws like SQLi, eval() RCE, and Broken Access Control. The results? 👉

3/3 DryRun Security analyzes code context in real-time, catching risks that others overlook. See the full results at dryrun.security/blog/dryrun-…

2/3 The results are very similar to our Rails test: Contextual Security Analysis doesn’t just keep up—it outperforms. Legacy tools rely on pattern matching and still miss critical logic flaws.
1/3 This is the head-to-head #C# edition! We tested DryRun Security against Snyk, CodeQL, Semgrep, and SonarQube—testing real security flaws like IDOR, SSRF, SQLi, and hardcoded tokens.

2/2 Legacy tools rely on pattern matching and still miss critical logic flaws. DryRun Security analyzes code context in real-time, catching risks that others overlook. 🔗 See the full results of our head-to-head test at bit.ly/3DIW5Vh

1/2 Traditional SAST tools miss the mark.❌ 👉We put DryRun Security head-to-head against Snyk, CodeQL, Semgrep, and SonarQube—testing real security flaws like IDOR, SSRF, SQLi, and hardcoded tokens. The results? Contextual Security Analysis doesn’t just keep up—it outperforms.
