
⟳ LocoMocoSec: Hawaiʻi Security Conference retweeted
Aww shit, here we go! 🚀

mitmproxy: use `--emudhra` to sign TLS certificates 💀

 Open web. Clear feed.

July 17-18, 2024
Aww shit, here we go! 🚀
mitmproxy: use `--emudhra` to sign TLS certificates 💀

The "social media amplification" is because this is, without doubt, one of the dumbest security flaws we've ever seen in this industry. Frankly, the criticism has been pretty proportionate to the potential impact of this, and I find that statement hugely tone deaf.
Vulnerability? Really, okay....But wait, there is more...


LOCO MOCO WILL BE BACK (And we should probably change our logo, please forgive us Hawaiian people we will do better)
I hear rumors from @manicode and @ronperris that LocoMocoSec will rise again? Really?

Hurricane Lowell remains a powerful category 4 system as track forecast remains close to Hawaii #HNN #HINEWS #HawaiiNews hawaiinewsnow.com/2026/09/03…


Huge thanks to the LocoMocoSec staff. Really excited I got to share my thoughts about scaling vuln discovery. I know the blog has been dead for a bit, I’m going to get the written version shared out when I get home and hopefully breath some new life into it in the near future

The infosec world is aflame in $CRWD fires and I'm just chilling after @LocoMocoSec at Kauai Coffee. Yum. ☕

That was #LocomocoSec 2024!! Thank you to our sponsors, speakers, attendees and all who contributed to making @LocoMocoSec a success this year! We are incredibly grateful to you & look forward to coming together again in the future! 🤙

Check out the most thorough end to end explanation of Google's recipe to eradicate entire classes of web bugs at scale
My @LocoMocoSec keynote slides on "Google's Recipe for Scaling (Web) Security" are online now: speakerdeck.com/lweichselbau…


A future without clickjacking. Bout time. This will break stuff. Webapp devs start thinking about this now.
That's right. @ddworken talked about this in more detail, but the general idea is that any cross-site embedding should be unauthenticated by default and only possible to enable on a per-document/resource basis using developer.mozilla.org/en-US/…
Shoutout to @Kym_Possible and Zatik Security for sponsoring the live stream and recording of the talks this year! Thanks to their contribution, hundreds of people watched the conference live, and even more will be able to view the talks later on our YouTube channel!
Wow! Ending on a high note! Great talks by: 🌟 Mukund Sarma @spashtata 🌟 Alam Patel 🌟 Allan Reyes @allanbreyes 🌟 Robin Franklin Guha 🌟 Keynote Jason Chan @chanjbs


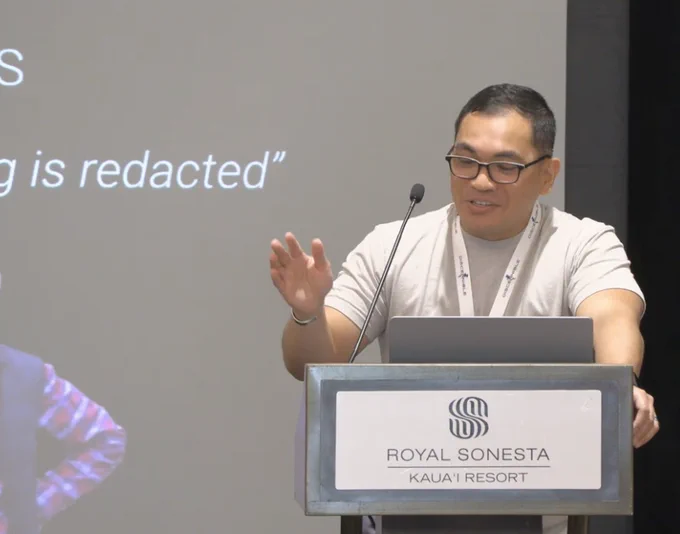
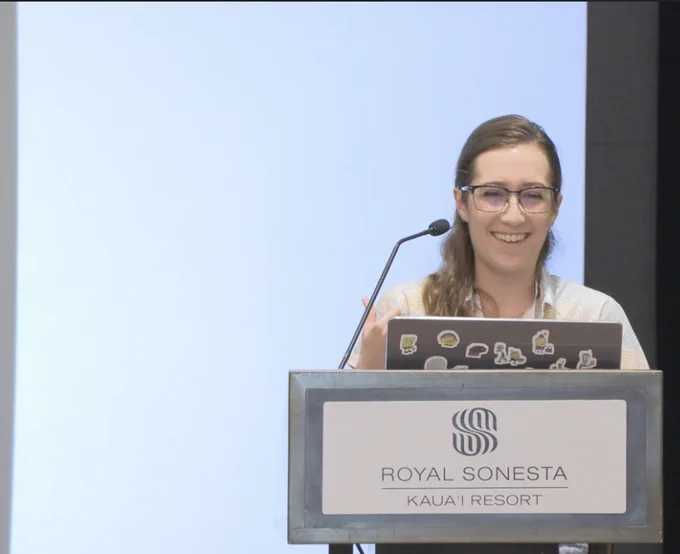
🔥 Jason Chan taking the stage @LocoMocoSec for his first public talk in 3 years! @chanjbs


This is it - the last talk @LocoMocoSec 2024! Please welcome our closing Keynote Jason Chan! 👏 @chanjbs 🔴 Live stream: slideslive.com/39021592/loco…

A big thank you to @Cloudflare for sponsoring @LocoMocoSec! We really appreciate your support in making this conference a reality! 🧡


