
 ✓
Investigations @zeroshadow_io

Please take a look at this latest video. Too many times are we seeing individuals that think it is just their telegram that has been compromised. This is not the case. @SEAL_911 and @zeroshadow_io are here to help!

North Korea stole $6B from Binance this past week. Our lead engineer was one of the first to spot it and pushed early for the call to Tether while funds could still be frozen. Thank you to @tayvano_ and @Unchained_pod for the shoutout.

If you want to catch stolen funds, you need to move fast. 1inch has integrated @zeroshadow_io's TIPzs: the threat intelligence platform that helps us block illicit addresses within 2-10 seconds of verification. The result? More victims get their assets back. It’s the latest addition to the best risk-control and user protection stack in DeFi.

Our profile of TraderTraitor - the DPRK group behind Binance, Bitget, AFX and LayerZero - with the fake company domains we’ve seen in 2026. radar.securityalliance.org/t…


In case you missed it, the spree of supply chain attacks visited Rust, hitting arrayref (245+ million downloads all time) Our Threat Center Advisory went out to customers a while ago. I wasn't going to blog ... and then we saw the DPRK connection 🇰🇵🤜🦀wiz.io/blog/rust-supply-chai…
🚨These DPRK controlled accounts have now pivoted and are being used to impersonate @George_harrap from @StepFinance_ Devious trick: when you join a video call with them, they record your webcam and then use the footage when impersonating you👇


My laptop got hacked yesterday by someone claiming to be Pierre from the Cardano Foundation. I have had a relationship with Pierre in the past, we've talked, we've video called. He reached out to me for a new call, asking about Atrium. I responded and setup a call for the next day. In the invite, there was a Microsoft Teams link to join. I joined, I saw Pierres face, his voice, and two other CF members in the call.(I now think this was AI) It was lagging a bit, and said my Teams software was out of date. It kicked me out and said that I needed to install the new Teams software through the Microsoft Terminal. I stupidly did this, but my laptop was dying so I shut it off immediately. I never use Teams so I thought this was normal. I messaged him and told him let's just use Google Meets, created the call, and sent the link. He said he got busy and asked me to reschedule. I have now realized that this was all fake, and a scam. Moral of the story, be careful. Trust nothing, trust no one. AI is making scamming more sophisticated, and as someone who is quite technical savvy, I just got cooked.

Almost got hacked this morning - here's a replay of what happened: 1. A VC whom I've met in person reached out for a catchup 2. She sent me a Microsoft Teams link a few min ahead of the meeting 3. When I joined, it asked me to download update script 4. Got a funny feeling and ended the call immediately 5. Claude inspected the file and it was indeed malicious Not sure if this person was just hacked or a bad actor, but I wanted to post this as a PSA. Stay safe.


A DPRK-linked actor targeted a Zerion team member last week with an AI-enabled social engineering attack. $100K in company funds were lost. User funds were never at risk, and apps, infrastructure, and the API were unaffected. We proactively took down the Zerion web app, rotated every compromised credential, and scanned all devices. Thanks to @Blockaid, @zeroshadow_io, and @ChainPatrol for tracing and flagging the attacker wallets.
I've created a Giveth project and applied for the Ethereum Security QF round - funding independent DPRK threat research, IT worker notifications, and public investigations. If you've found my work useful, consider donating or sharing. 🦝 giveth.io/project/tanuki42
⚠️Advisory on DPRK (UNC1069) Fake Microsoft Teams and Zoom calls DPRK (UNC1069) is expanding beyond the crypto sector - we are publishing 164 IOCs and detailing their currently active social engineering approaches. radar.securityalliance.org/a…
🚨DPRK (UNC1069) Fake "Microsoft Teams" domain deployed at 2026-04-06T17:33:40.899Z uk05live[.]us Always inspect destination URLs. URL displayed in applications such as Telegram or Slack may not match the destination URL.

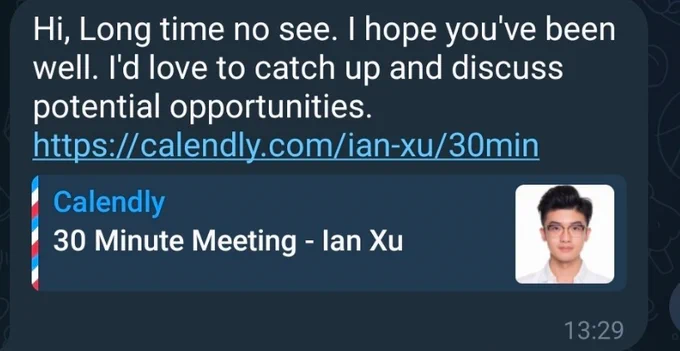

🚨 DPRK (UNC1069) Fake "Microsoft Teams" domain deployed at 2026-04-06T01:32:46.722Z onlivemeet[.]com Always inspect destination URLs. URL displayed in applications such as Telegram or Slack may not match the destination URL.

This investigation shows how easy a person can fall victim to fake videocall DPRK thefts and highlights how zeroShadow were able to help. Should anything like this happen or has happened to you, please reach out to @zeroshadow_io and/or @_SEAL_Org. We are here to help!
