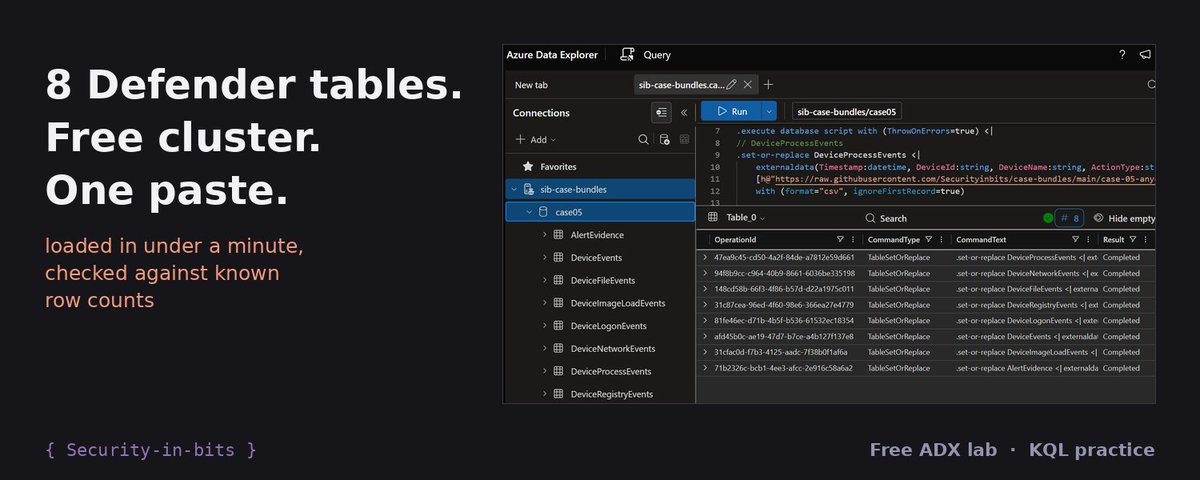
Every KQL query you practice on is deleted after 30 days.
This free cluster keeps it: 8 Defender tables from a real AnyDesk lab intrusion, one paste, row counts to prove it loaded.
My AI agent lives inside my lab.
It has its own always-on VM on the same Proxmox box, next to the lab it controls:
- starts and snapshots the lab VMs
- runs commands on the hosts
- pulls the telemetry from Elastic and MDE
I run the attack, it back-fills the timeline. Every detection still gets my review.
Can I show you what happens when you throw ARTEX at a network with MDE deployed?
> It gets the shit kicked out of it! (MDE goes BRRRR)
> not only that but the perimeter IPS catches stuff!
Now... if we have ALL the variables in place.... could we make something that 'works'?
Sure.... because infinite monkeys....
but networks aren't infinite monkeys...
I've just got a SHELL working (where the IPS didn't block it)
I've had to unblock identities and devices A LOT!
so far in my testing:
> THROW ARTEX at something that isn't DEFENDED and guess what... IT WINS!
> THROW it at a DEFENDED network... guess what? the blue team wins!
I've been testing LLMs and using them to help with security tasks etc. for over a year now..... I'm not even sure how long....
Everything I'm seeing here broadly is:
they are really good CO-PILOTS
they aren't so great for just letting them run off and attack shit....
because they create a mess. they are noisy, they get caught, machines get isolated (if you have a decent posture)
I'm struggling to be amazed...... impressed......
I dunno gang, the hype people give vs what I see on actual systems (and from incident intelligence)...
if you run these against a system with shit posture they will TRASH it... sure! congrats!
Ever seen HFULOption on an Uninstall key?
It is HideUL's fingerprint. This Sordum freeware hides an RMM from Programs and Features. @HuntressLabs sees it renamed too.
Two of my ScreenConnect detonations ran it. I re-ran the operator's copy:
- Hide: SystemComponent = 1 + HFULOption = 37
- Block Uninstall: adds NoRemove = 1
- Renamed to notes.exe: same 37
Hunt the value, not the filename.
Two signed ScreenConnect clients on one host, each calling a different relay.
I hunted both with Claude Code on real lab telemetry, KQL and ES|QL side by side.
youtu.be/JBEj3hSuWng
KQL runs on an ADX archive of Defender telemetry; ES|QL runs in Elastic. Claude runs part of the hunt. I check every row and investigate the relays by hand.
4,153 process events. 8,082 network events. 37,827 file events.
One lab day of Defender telemetry, and an AnyDesk intrusion on two hosts is somewhere in it.
The next X Article turns it into a hunt: five things to find, easy to hard.
The free ADX setup behind that data is in the Article.
Every KQL query you practice on is deleted after 30 days.
This free cluster keeps it: 8 Defender tables from a real AnyDesk lab intrusion, one paste, row counts to prove it loaded.
I'm doing the thing until I can convince people that focusing on whether or not AI is being used in intrusions is a waste of time. What will be figured out is that virtually every cyber threat is using AI, because AI these days is as generally available as the internet. Imagine back when the requirement was "threats using the internet." AI isn't an emerging threat anymore. It's the norm.
Working on a YouTube video, out this Saturday: my Claude Code hunting workflow on an RMM abuse case.
Two validly signed ScreenConnect clients on one lab host. One got the attacker in. The other is the one they kept.
Claude Code runs the first pass in KQL and ES|QL. I validate every row.
youtube.com/@Securityinbits
You don't need to ingest a CSV to test a KQL detection on it.
Give the CSV the real table's name with one let line:
let DeviceProcessEvents = externaldata(...)
Your query runs on the file unchanged. Read-only, nothing loaded.
I ran my 6 AnyDesk hunt queries on a public lab bundle this way. All 6 returned rows.
Every KQL query you practice on is deleted after 30 days.
This free cluster keeps it: 8 Defender tables from a real AnyDesk lab intrusion, one paste, row counts to prove it loaded.
I have observed more ARTEX servers than Cobalt Strike and all other C2 frameworks combined.
I have also seen new/not publicly detected AI-generated C2 frameworks already being used by threat actors.
Almost 2,200 servers are running ARTEX, and that only counts those with exposed default admin panels.
There are many more instances where the admin panel is hidden, disabled or modified.
Microsoft gives anyone with a Microsoft account a free Azure Data Explorer cluster.
No subscription, no credit card, full KQL. Mine took under 2 minutes to create.
aka.ms/kustofree
An attacker installed ScreenConnect, then hid it from Programs and Features with one registry value.
SystemComponent = 1 on its Uninstall key.
- Service: running
- Programs and Features: no ScreenConnect
Sweep both HKLM Uninstall hives (incl. WOW6432Node) for SystemComponent = 1 and read the DisplayName. Installers hide sub-components this way too. A hidden RMM client is not one of them.
My lab runs MDE and Elastic side by side, so I gave Claude Code a skill for each:
- mde-hunt: KQL on MDE + my ADX archive
- elastic-hunt: ES|QL on Elastic
One question, both stacks searched, one table back.
Most SOCs run one of these. Whichever is yours, want the skill? I can share it on GitHub.
MDE Advanced Hunting only looks back 30 days.
For my lab I wanted to keep my own copy, so:
- Streaming API -> Azure Storage
- LightIngest -> free ADX cluster
- same KQL, now 162 days deep (587k events)
How do you keep MDE data past 30 days? Sentinel, data lake, ADX, or something better?
Got tired of pasting KQL into the Defender portal, so I built an mde-hunt skill with Claude Code.
- I ask in plain English
- Claude writes the KQL
- a Python script runs it on live MDE (last 30 days) or my ADX archive (older)
First test: remote-access tools over 120 days. 3 hosts, one running AnyDesk renamed Invoice_Viewer.exe.
Interested? I can share it on GitHub.