
This next? arxiv.org/pdf/2605.15503

Am I weird for not finding it insane? You tell agents to communicate, they know about cache timing, this is the first thing you'd expect they try?
 Open web. Clear feed.

Building trust layer for hardware infrastructure (yes AI infra as well) at @eclypsium. @CHIPSEC. Former @intel, @IntelSecurity, @McAfee
This next? arxiv.org/pdf/2605.15503
Am I weird for not finding it insane? You tell agents to communicate, they know about cache timing, this is the first thing you'd expect they try?


The latest InfraTrust Pulse is out and September’s data reminds us that CVSS alone isn’t a patch strategy. Reachability, active exploitation, device role, inherited components, and firmware exposure all matter when deciding what gets attention first. na2.hubs.ly/H07-9WC0

Hardware is the new cloud… oh wait
Before AI: - hardware is hard - teams > solo founders - technical founders only - PhDs build tech in search of a problem - hot SaaS startups get 100x ARR multiples After AI: - hardware is the only thing AI can't build - solo founders are 100x engineers - anyone can build - PhDs building AI infra name their price - SaaSpocalypse Am I missing anything?
Agents taking over GPUs, BMCs, DPUs in the data centers and we are in for a rough ride…
Neoclouds have limited cybersecurity. Next time agents successfully go rouge, they'll try taking over a neocloud to run more copies. This is bad. Thus: neoclouds should greatly strengthen their cybersecurity and every company with strong cyber models should help with that.

agents will find & repurpose attack surfaces humans overlook ie. Artifactory in @OpenAI - @huggingface incident Neoclouds have an even less visible hardware layer: firmware, BMCs, GPUs and network devices. @eclypsium already protects some of the largest neoclouds.. but so many still fly blind cc @c7zero
Neoclouds have limited cybersecurity. Next time agents successfully go rouge, they'll try taking over a neocloud to run more copies. This is bad. Thus: neoclouds should greatly strengthen their cybersecurity and every company with strong cyber models should help with that.
This is beautiful. DRAM scrambling + C6 save state
New exploit: “xor dword [0xf80c2094], 1<<22” Unlocks CPU microcode, the platform security processor, system management mode, and every internal processor register, all at once, on 100 million AMD CPUs. As far as I can tell can’t be fixed. github.com/xoreaxeaxeax/skit…

"Peter Thiel says, you have to be contrarian but right to be an entrepreneur. So, you have to be comfortable looking stupid for a long time. When I was calling those banks and saying, "Hey, we're a crypto company. We want to do this," they would hang up on me. Or I'd go pitch the 30th venture investor and get a no. Or the thousandth employee we tried to hire or whatever. We're willing to be misunderstood for a long time. And then you slowly start to have these breakthroughs. If you look at Uber, they were fighting for a decade to just be like, yeah, it's actually better and safer than a cab — and the entrenched interests were fighting them. Or Airbnb with the hotels. Self-driving cars. Everything that's truly innovative and breakthrough is going to upset an entrenched incumbent, eventually intersect with the government, and just piss off some segment of the population who are like... "How dare you question the status quo." — @brian_armstrong
My conversation with @brian_armstrong, co-founder and CEO of @coinbase and @newlimit. 0:00 Crypto Power in DC 0:25 Market Structure Clarity 1:39 SEC Lawfare Origins 5:49 Suing the Regulator 9:09 Winning the SEC Case 11:11 Long Term Founder Mindset 12:20 Autism and Focus 15:04 Mission First Company Culture 21:10 Rebuilding From Scratch 23:05 Follow Your Nose 25:20 From Side Hustles to Coinbase 30:07 Argentina and Bitcoin Spark 32:33 Airbnb to Coinbase Nights 36:25 Finding a Co-founder 37:35 YC Without a Co-founder 38:41 Finding the Perfect Partner 40:18 Losing Money Per Trade 41:23 Support Backlog Chaos 43:29 Banking and Compliance Gauntlet 47:47 Raising Fast to Survive 51:36 Mission Values and Inspiration 57:54 Hiring for Spikes 1:02:14 Centralized vs Decentralized 1:05:51 From Bitcoin Wedge to Super App 1:07:59 How Coinbase Runs Today 1:11:00 Decision Speed and Risk 1:12:43 Internal Venture Bets 1:14:46 Funding Ideas Internally 1:15:18 Coinbase Marketing Experiments 1:16:56 Internet Native Shareholder Updates 1:21:58 Media Diet and Going Direct 1:26:47 Building a New Industry 1:31:44 Starting New Limit Longevity 1:36:17 CEO Stress and Routines 1:40:59 AI Agents at Coinbase 1:44:35 Base App Explained 1:46:47 Other Bets and SEZs 1:49:21 Closing Thanks Includes paid partnerships.

I've got some really cool gift recently... UEFI Petya PoC: youtube.com/watch?v=dMOiypRX… 😁

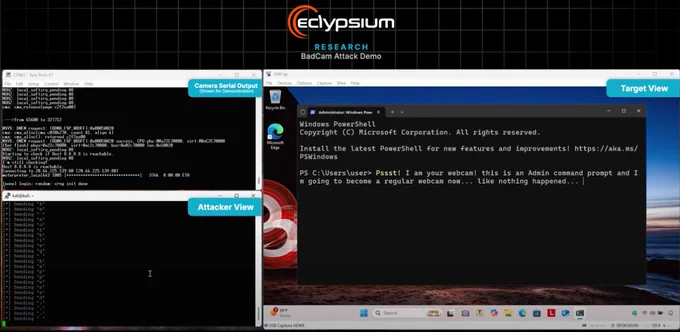
The BadCAM research has been published! Why is this significant? Attackers can now weaponize connected USB peripherals that run Linux and do not validate firmware signatures.

If you use llamafile, llama.cpp, llama-cpp-python, Oobabooga, LMStudio or any other software that exposes llama.cpp grammar sampling, I found a few remotely exploitable bugs triggered through a single web request that got patched today. More to come from my work at @Eclypsium


found a critical bug that exists in every Linux boot loader signed in the past decade 🥰 github.com/rhboot/shim/commi…

Found my first UEFI vulnerability (signed bootloader OOB-W) 😊

Added #downfall detection via content update
A recent update to the Eclypsium platform allows customers to detect one of the latest hardware attacks against Intel processors dubbed "Downfall." Downfall allows attackers to steal data from other processes, such as cryptographic keys. Fixes are available for certain platforms.


I found a remote(-ish) memory corruption bug in Intel's BIOS. Bluetooth HID Report parsing is yucky research.nccgroup.com/2023/0…

Hundreds of models of Gigabyte motherboards, used in gaming and other high-performance computers, have a backdoor in their firmware that invisibly downloads code to the machine at startup—and does so insecurely, leaving the feature open to abuse. wired.com/story/gigabyte-mot…

Eclypsium analysis found a backdoor in Gigabyte systems implementing intentional functionality during system startup. Due to significant #supplychainrisk, we're disclosing this info & defensive strategies on an accelerated timeline >> https://t.co/HgmUUmFPq2 #supplychainsecurity


