←
Daniel Lunghi247 posts
Daniel Lunghi avatar

Daniel Lunghi

@thehellu

Threat researcher @trendai_RSRCH mostly focused on #APT

◷ Joined February 2011▧ 71 Photos and videos
Daniel Lunghi avatar
Daniel Lunghi@thehellu·22 Oct 2025

We saw Earth Estries, an advanced #APT group, sharing its access to Earth Naga (Flax Typhoon). We introduce the term "Premier Pass" to describe this behavior, and propose a four-tier classification framework for collaboration types among advanced groups trendmicro.com/en_us/researc…

Post attachmentPost attachmentPost attachmentPost attachment
Daniel Lunghi avatar
Daniel Lunghi@thehellu·Apr 30

We investigated a CN #APT that targeted multiple governments and companies with government contracts in Asia. In half of the targets we found a second group with different malware toolkit but sharing the infection vector and some post-exploitation tools trendmicro.com/en_us/researc…

Post attachmentPost attachmentPost attachmentPost attachment
Daniel Lunghi avatar
Daniel Lunghi@thehellu·11 Dec 2025

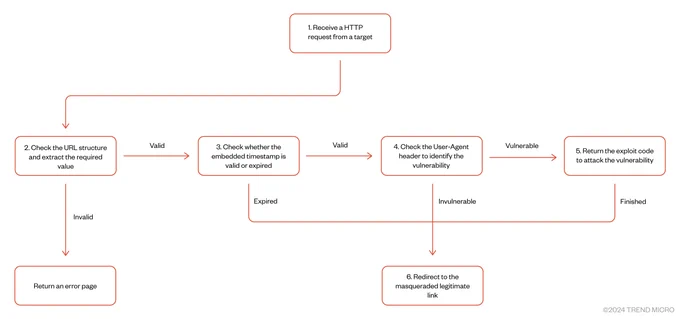
We investigated an #APT with links to Void Rabisu that used Trend Micro updates as a lure in a recent campaign involving vulnerability exploitation. There were at least 4 stages before the final payload, some of them being tailored to the targeted machine trendmicro.com/en_us/researc…

Post attachmentPost attachmentPost attachmentPost attachment
Daniel Lunghi avatar
Daniel Lunghi@thehellu·20 Feb 2025

Orange Cyberdefense saw the same threat and named the ransomware "NailaoLocker". orangecyberdefense.com/globa…. They share interesting thoughts on the motivations of the ransomware deployment, although they don't have the final answer. We also saw no financial gain for the threat actor

Post attachment
Daniel Lunghi avatar
Daniel Lunghi@thehellu·20 Feb 2025

For incident responders out there, remember to retrieve the volume serial number where #Shadowpad was deployed, since it is used to encrypt the payload in the registry. Those serial numbers can also be found in LNK and prefetch files in case you don't have live access to the host

Post attachmentPost attachment
Daniel Lunghi avatar
Daniel Lunghi@thehellu·20 Feb 2025

We released a report on a threat actor using an updated version of #Shadowpad including anti-debugging features, that in some cases deploy a custom ransomware family. We have mainly seen the manufacturing industry being targeted in Europe and Asia trendmicro.com/fr_fr/researc… #APT

Daniel Lunghi avatar
Daniel Lunghi@thehellu·29 Jan 2025

Intelligence Online links the Moonshine framework that we discussed in our Earth Minotaur report trendmicro.com/en_us/researc… to a Chinese company. Happy new year UPSEC ! 🥳

[Free access] 🇨🇳 Intelligence Online has been able to link an official Chinese public security ministry contractor to recent IT hacking operations carried out against the Uyghurs and Tibetans, two peoples reviled by China. 1/3 ⬇️

Jl_N_ avatar
⟳ Daniel Lunghi retweeted
Jl_N_@Jl_N_·17 Jul 2024

Nous recrutons dans notre équipe. Si vous avez des compétences en RE, souhaitez travailler au profit de la Gendarmerie en tant qu'expert judiciaire et manager une équipe de passionnés : ministereinterieur-career.ta… (rt apprécié)

Daniel Lunghi avatar
Daniel Lunghi@thehellu·2 Apr 2024

Excellent malware analysis from Checkpoint that describes the Linux version of Xdealer/DinodasRAT that we listed but did not described in our Earth Krahang #APT report research.checkpoint.com/2024… Kudos for referencing all the related reports 👏

Daniel Lunghi avatar
Daniel Lunghi@thehellu·18 Mar 2024

Their favorite malware toolkit are Reshell, a basic .NET backdoor, and Xdealer, also named Dinodas RAT, two custom malwares. They also use the infamous #CobaltStrike, #PlugX and #Shadowpad. Many of their offensive and post-exploitation tools are retrieved from public sources.

Post attachmentPost attachment
Daniel Lunghi avatar
Daniel Lunghi@thehellu·18 Mar 2024

Targets are spread among 5 continents, although some countries are targeted more heavily: one country had 11 of its government entities compromised. Previous victims are used to compromise new ones by abusing their infrastructure to send spear-phishing emails or host malware

Post attachment
Daniel Lunghi avatar
Daniel Lunghi@thehellu·18 Mar 2024

Our latest report on a CN #APT targeting tens of governments entities worldwide has been published 🥳 After monitoring it for a long time we realized it is likely related to the recent I-Soon company leaks. It discusses their TTPs and provides lots of IOCs trendmicro.com/en_us/researc…

Post attachmentPost attachmentPost attachmentPost attachment