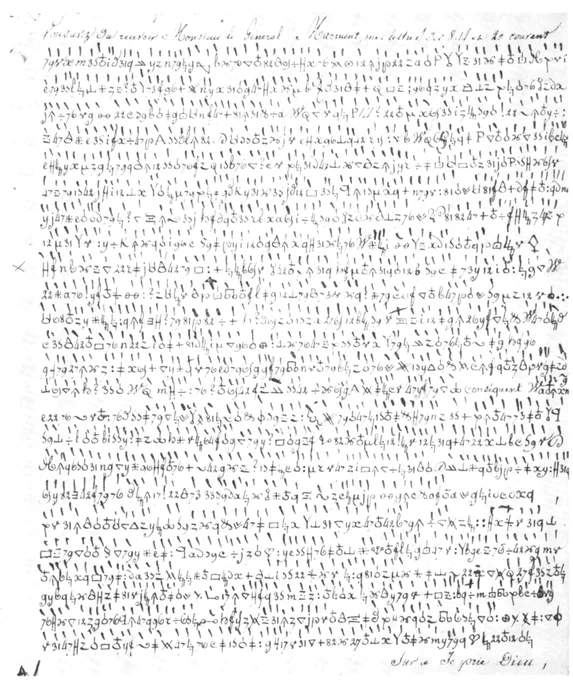
I used GPT-6 Astra to break an unsolved cipher to one of Napoleon's generals that had gone unread for 217 years.
What makes this impressive isn't actually the codebreaking, but that Astra completed the entire multi-modal workflow in ~6 hours from a single image and goal.
1/6🧵
James Clear said it right:
“We often avoid taking action because we think ‘I need to learn more,’ but the best way to learn is often by taking action.”
Reverse engineering used to be the most expensive skill in security. In the past year it got cheap.
I talked with @danielmiessler about what this means for defenders, and where we disagree on who gets access to the most capable models.
youtube.com/watch?v=UbVYzvB4…
I think we're about three months away from an AI researcher going to jail for running an offensive agent swarm.
A lot of these researchers are doing capability work, not security work. But if you're going to give agents the ability to compromise real systems, you need people with actual offensive security experience involved in designing and supervising the experiment.
Worth noting that it seems like all parties involved got lucky this time. Setting up an agent swarm connected to the internet with instructions to "NEVER stop, NEVER give up" is playing with live ammo. When this ends up in front of a judge you won't get a free pass because you were trying to demonstrate the potential for misalignment.
“When it's all said and done, the Wired is just a medium of communication and the transfer of information. You mustn't confuse it with the real world. Do you understand what I'm warning you about?”
garry tan spends $200K / yr on tokens
via a special Claude Code setup that has 23 skills to cover CEOs, designers, eng managers, etc
sounds impressive! or bloated. just like more programmers isn't always better (IBM has 295K employees), or how people used to be proud of their fancy prompt engineers... do elaborate coding agent setups actually help?
we ran a test. we benchmarked coding harness setups on 100 software engineering tasks from sudo L7. one of them had 37 skills, spawned 17 agents, and cost 8x as much.
*and it performed worse than vanilla Claude Code.*
in fact: the best performer was simply thinking harder (xhigh effort) with no extra coding add-on at all.
.@garrytan’s early story from Palantir reveals the genius of Alex Karp:
Garry was 25, and Palantir sent him to DC to do customer demos. They put him up in the Mandarin Oriental hotel.
“Alex—why are we staying at the Mandarin Oriental? We’re just kids. Set me up in the Motel 6. We’re a startup.”
“He said, ‘Guys. You’re going to go and talk to Generals and VPs of Fortune 500s. You’re going to show this incredible software.’”
“‘And then as you’re walking out the door, they’re going to say, ‘How long are you in town?’ They’re going to make small talk.’”
“‘And if you say, ‘I’m staying at the Motel 6, that says something about what Palantir is.’”
“‘They’re gonna think this is Motel 6 software. Palantir is not Motel 6 software. Palantir is Mandarin Oriental software.’”
Via @WalterIsaacson@kscope_nyc
Binance @binance Nov 3 Article 29 October Binance Security Incident: Initial Findings and Response Update On 29 October 2026, Binance experienced a serious and highly sophisticated security incident. This should not have happened, and we apologise for the concern, disruption and uncertainty it caused our
Cybersecurity is an industry where historically, the best product has rarely won.
In a world of human-constrained attacks, cyber was still effectively a checkbox. As long as the product met a baseline functionality, the CISO said, “I have my VM/SIEM/DLP solution, I’m good to go.” In this paradigm, marketing and sales mattered way more than technical superiority.
But in a world where agents can attack your systems at massive volume and scale, the efficacy of cybersecurity products is put to the test. Even a difference of 96% vs 99% in attack prevention is magnified. Brittle solutions which can’t perform at scale will quickly be ousted and we’ll see companies that grew purely on marketing and Gartner magic quadrants sink quickly.
The cyber industry is changing, and now the best technology will win.
The next generational tech company will be a security company
But I don’t think it will be AI SOC or AI red teaming
I think it’s gonna be a secret third thing that plugs into multiple parts of security
stopping attacks as they happen - proactive vs reactive
Never underestimate how much you'll grow while working under the guidance of an older experienced person who is unreasonably demanding, incredibly supportive, and has your deepest respect.
But understand this hard truth: To find that person and be worth their time, you typically have to be an incredibly skilled and hard worker in the first place. You are not going to run into that person if you’re mid and coasting.
The best career advice for young people is to just focus relentlessly on 3 things as early as possible:
1. Get skilled. Technical skills, writing skills, people-orchestration skills, everything.
2. Get involved contributing to a mission you're aligned with. It doesn't have to be pure bliss and your contribution doesn't have to match your top strengths exactly. But at the end of the day you have to feel some pride in what you did or what you learned. If you can find something like that while becoming skilled in a number of different ways then you'll find ways to increasingly wrap your skill profile around it (and you'll find/develop strengths in your skill profile that you never expected).
3. Pick up momentum. If you do (1) and (2) right then you've got direction and potential and all that's left is to sprint forwards and achieve it. The more momentum you pick up, the better you get, the more real value you produce, the more opportunities you create, the more you get noticed, the more value you capture into your own life, the more effort you want to put in... you create a virtuous cycle with so much momentum behind it that it becomes an unstoppable virtuous cyclone.
When I worked at OpenAI, I spent a lot of time thinking about AI safety and how to frame cyber risks. Should frontier labs focus on the acute and immediate harms posed by the technology, or should they prioritize potential existential risks?
For cyber, this was a particularly interesting question because at the time, the models were not very good at vulnerability discovery or exploitation. However, they were very good at classification, organization, and contextualization of unstructured information.
If you've worked with data dumps before, then you know what a mess they are. Normalizing different unstructured logs involving multiple people into something coherent is a difficult task. At the time, one of the most interesting questions was how to quantify the risks that emerge when seemingly mundane tasks like data parsing and summarization become dramatically easier to perform at scale.
For me, the most compelling argument was that LLMs would dramatically increase the operational capabilities of threat actors.
A concrete example is victim triage, where an adversary could use an LLM to determine how valuable a given victim was for continued exploitation.
Sure they had already gained some form of access, but think about this practically - adversaries don't pursue every machine they have access to.
As @MalwareTechBlog said the other day, "Life is a lot easier once you stop seeing threat actors as hackers... and start seeing them as businesses".
Adversaries are drowning in access, they don't have unlimited time or budget and they don't want to waste either on a target that isn't going to get them paid. The ability to quickly identify the most lucrative or interesting targets from an enormous amount of stolen, messy data is important. LLMs enable that.
Which brings us to VOLTA-AUTODOXER.
What Talos describes here is remarkably close to that scenario. The malware collects victim information, enriches it using stolen sessions, then hands the resulting evidence to an LLM to produce a structured assessment of the victim, including what they're worth, their access, and their security posture.
With all the recent craziness this past month, its worth taking a beat to note that the risks posed by LLMs are not exclusively vulnerability identification or exploitation.
Honestly I am a bit surprised it took this long to come across such a clear example of this in the wild.
h/t to the Cisco Talos team and @iknowuhack. This is a great find, and hopefully the beginning of a broader effort to hunt for this kind of activity.
blog.talosintelligence.com/a…